
 In 30 Seconds
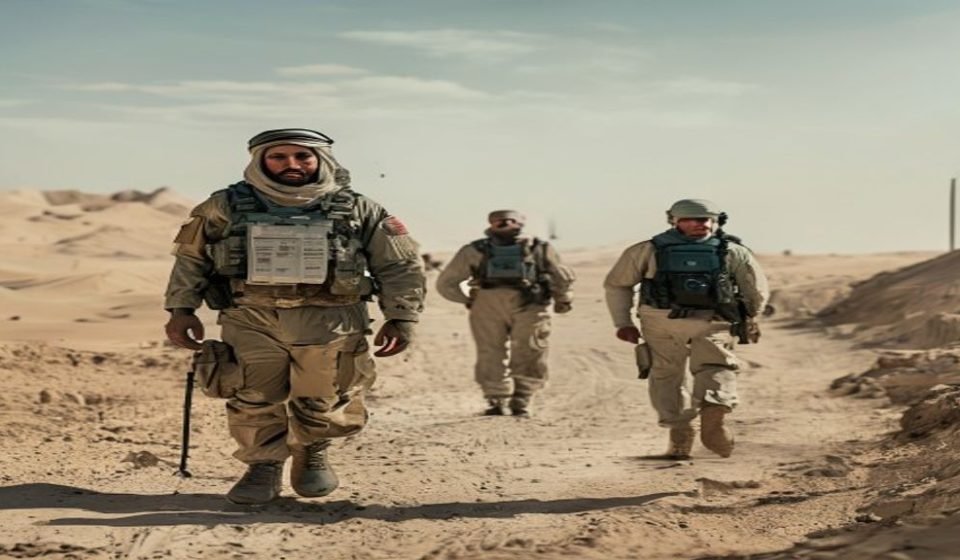
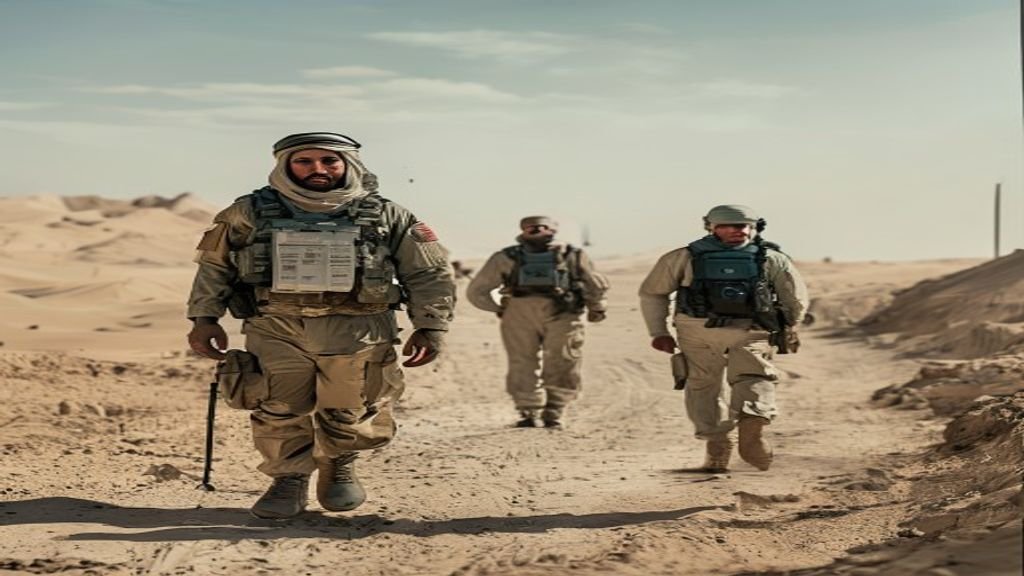
Recent reports have unveiled a sophisticated cyber espionage campaign, allegedly orchestrated by Iran, targeting US military personnel across the volatile regions of the Gulf and the Middle East. This insidious operation reportedly exploited everyday technologies, including data roaming services and advertising technology platforms, alongside inherent vulnerabilities within global mobile networks, to meticulously track the precise locations of American service members. The findings, brought to light by NDTV, underscore a deeply concerning intersection of consumer technology and national security threats, painting a stark picture of how widely available digital tools can be repurposed for surveillance against military forces.
This revelation has cast a fresh spotlight on the pervasive risks associated with modern digital infrastructure, particularly for individuals operating in sensitive environments. The intricate methods employed by elements with reported ties to Iran illustrate a calculated exploitation of systems designed for connectivity and commerce, transforming them into instruments of clandestine tracking. Such activities pose a significant challenge to the security protocols in place for deployed personnel, prompting urgent questions about the resilience of existing safeguards against such technologically advanced forms of espionage.
Background
The mechanisms behind this tracking operation were reportedly complex, comprising multiple layers and cleverly integrated. At its core, the scheme capitalized on the fundamental architecture of mobile communication: data roaming. When US military personnel used their smartphones abroad, their devices would connect to local mobile networks. The process of routing this international traffic, including location data, through various telecommunication providers allegedly provided an avenue for interception. Reports suggest that this data, often shared between carriers for billing and network management purposes, was either compromised or exploited by the actors involved.
Beyond traditional network weaknesses, advertising technology, or ad tech, played a surprising and critical role. The vast ecosystem of online advertising relies on gathering extensive user data, including location information, to deliver targeted advertisements. It appears that entities with ties to Iran managed to tap into this commercial data stream, potentially through compromised ad tech platforms or by leveraging data brokers who aggregate such information. This allowed them to pinpoint the geographical whereabouts of military personnel, transforming seemingly innocuous digital footprints into actionable intelligence. The confluence of these methods data roaming, ad tech, and the existing vulnerabilities within the global mobile network infrastructure created a powerful surveillance apparatus capable of tracking the exact location of US military smartphones across a wide geographical expanse. This underscores the alarming reality that even without direct hacking of individual devices, location data can be extracted and weaponized through the broader digital environment.
Timeline of Events
The first public disclosure regarding this concerning development emerged on July 15, 2026, at approximately 8:05 AM. It was at this juncture that news outlets began reporting on how Iran had allegedly utilized data roaming capabilities, advertising technology, and vulnerabilities within mobile network infrastructure to monitor and track US military personnel stationed across the Gulf and the Middle East. This initial reporting immediately brought to the forefront the innovative and unsettling methods being employed in the realm of cyber espionage against military forces in sensitive regions.
Why It Matters
The ramifications of this alleged Iranian operation extend far beyond mere privacy concerns for individual service members; they strike at the very heart of national security. The ability of an adversary to precisely track the movements of military personnel presents an unacceptable risk, potentially exposing classified operations, troop deployments, and individual lives to imminent danger. Such granular location intelligence could be used to anticipate movements, plan ambushes, or compromise the safety of personnel during sensitive missions.
Moreover, this incident highlights a critical vulnerability in the digital perimeter surrounding military operations. While physical security measures are often robust, the reliance on personal smartphones and the ubiquitous nature of global mobile networks introduce an unforeseen vector for sophisticated espionage. It compels a re evaluation of acceptable risks associated with personal device usage in operational zones and raises questions about the responsibility of telecommunications companies and ad tech firms to safeguard sensitive data that could have profound geopolitical consequences. This incident could also escalate tensions in an already volatile region, as the United States will undoubtedly view such tracking as a hostile act requiring a strong response to protect its forces.
What Could Happen Next
In the immediate aftermath of these revelations, the United States is likely to launch comprehensive internal investigations into the extent of the tracking and the specific vulnerabilities exploited. This could involve an intensified review of the security protocols governing personal device usage among military personnel, potentially leading to stricter guidelines or outright bans on certain smartphone functionalities or network usage in areas posing significant risk. There may also be increased efforts to work with telecommunication providers and international partners to identify and mitigate the network weaknesses that facilitated this espionage.
Beyond internal measures, the US government might consider diplomatic or retaliatory cyber actions against the entities or individuals responsible for the tracking. This incident could also spur broader discussions within NATO and other allied nations about collective defense strategies against advanced cyber espionage, particularly those leveraging commercial data streams. Furthermore, there could be a push for greater regulatory oversight of the ad tech industry and data brokers, emphasizing the need for robust data protection measures to prevent such sensitive information from falling into adversarial hands. The long term implications could reshape how military forces operate digitally in deployed environments, emphasizing security by design in all digital interactions.
Frequently Asked Questions
How did Iran reportedly track US military personnel?
According to reports, Iran used a combination of data roaming services, advertising technology platforms, and existing vulnerabilities within global mobile networks to track the exact location of US military personnel’s smartphones.
Which geographical areas were primarily affected by this tracking?
The alleged tracking operation specifically targeted US military personnel operating across the regions of the Gulf and the Middle East.
What type of data was Iran reportedly seeking through these methods?
Iran was reportedly seeking precise location data from the smartphones of US military personnel, enabling them to ascertain the exact whereabouts of individuals and potentially troop movements.